
25 editable reference diagrams
Security Architecture Diagrams
Security architecture diagrams make identity, trust boundaries, policy decisions and audit paths explicit. These references cover authentication, authorization, federation and the operational systems protecting credentials and sensitive data.
Choose the trust question first: who is calling, which action is allowed, or how a credential is protected. These are separate checks. Adapt the protocol flow to the actual client and threat model, and verify configuration against authoritative specifications before deployment.
Choose a diagram for your design question
Open a reference to inspect its component flow and trade-offs, then adapt it in the browser-local editor. Manual editing does not require login; AI generation and account storage do.
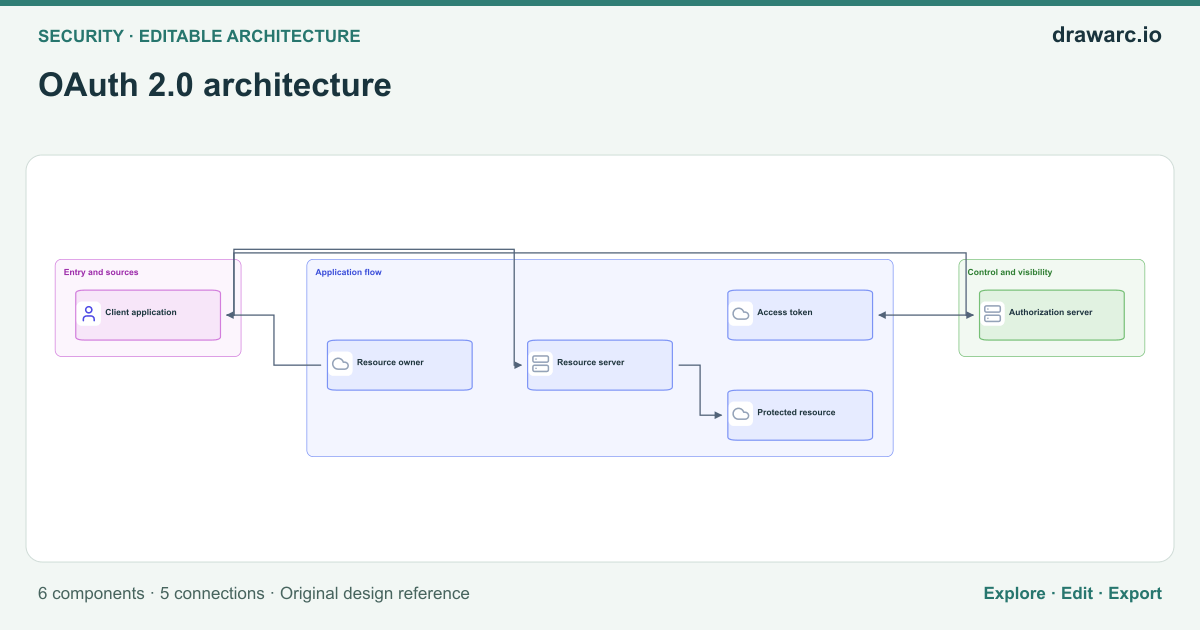
OAuth 2.0 architecture
Select a grant appropriate to the client.
6 components · 5 connections
Explore oauth 2.0 architecture →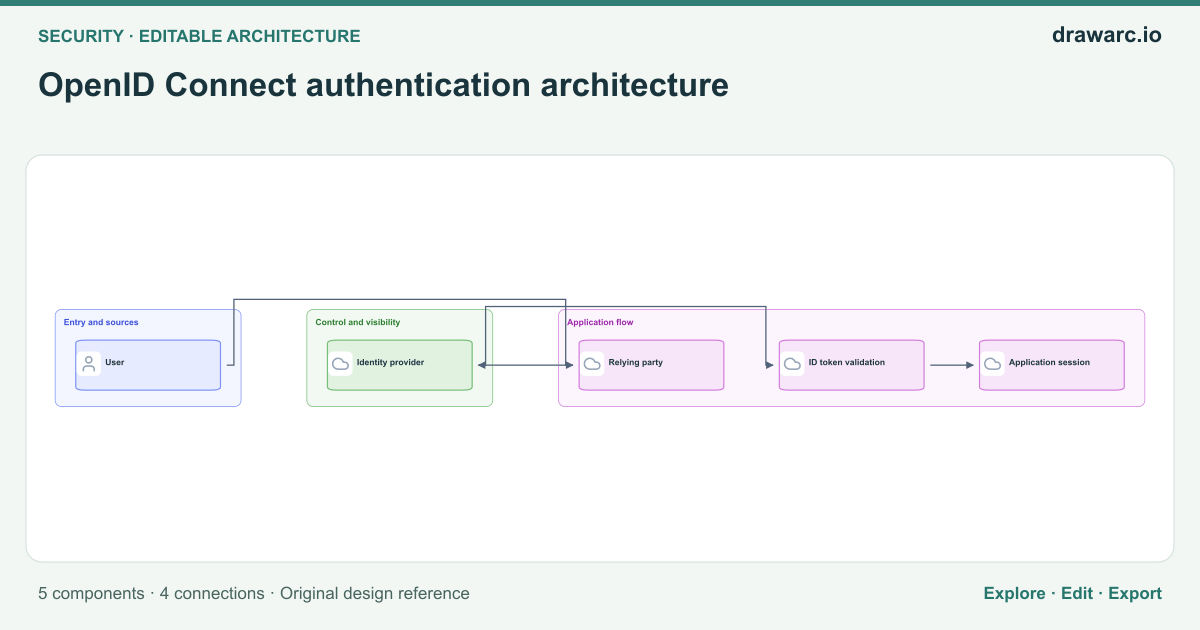
OpenID Connect authentication architecture
Validate issuer, audience, signature and nonce.
5 components · 4 connections
Explore openid connect authentication architecture →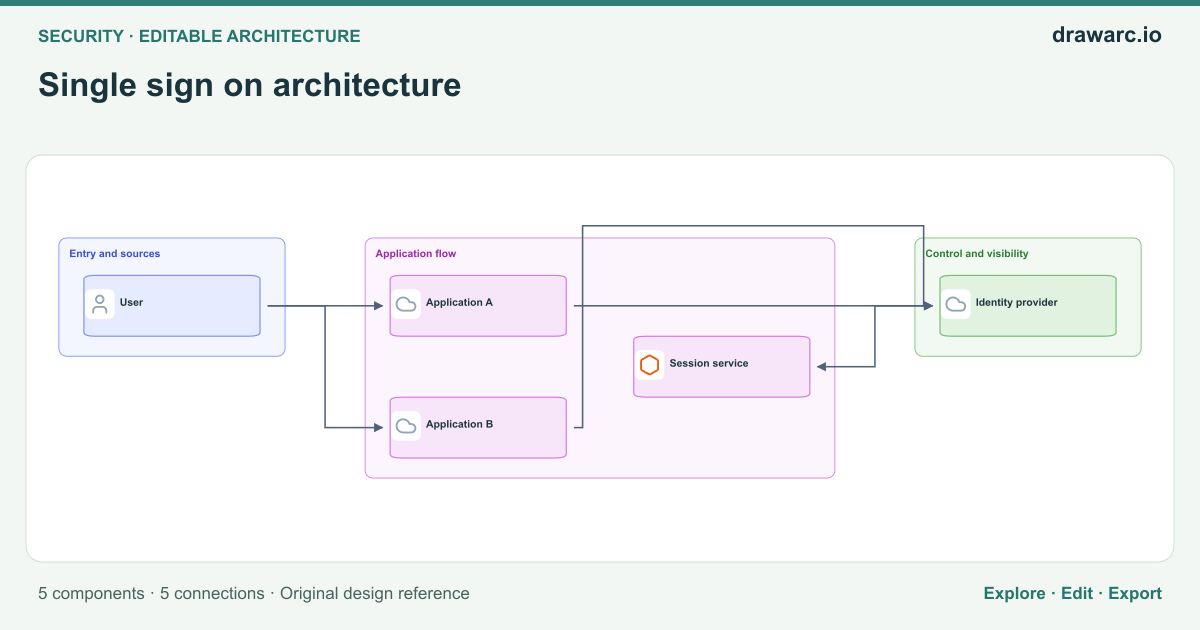
Single sign on architecture
Shared sign-in does not imply shared authorization.
5 components · 5 connections
Explore single sign on architecture →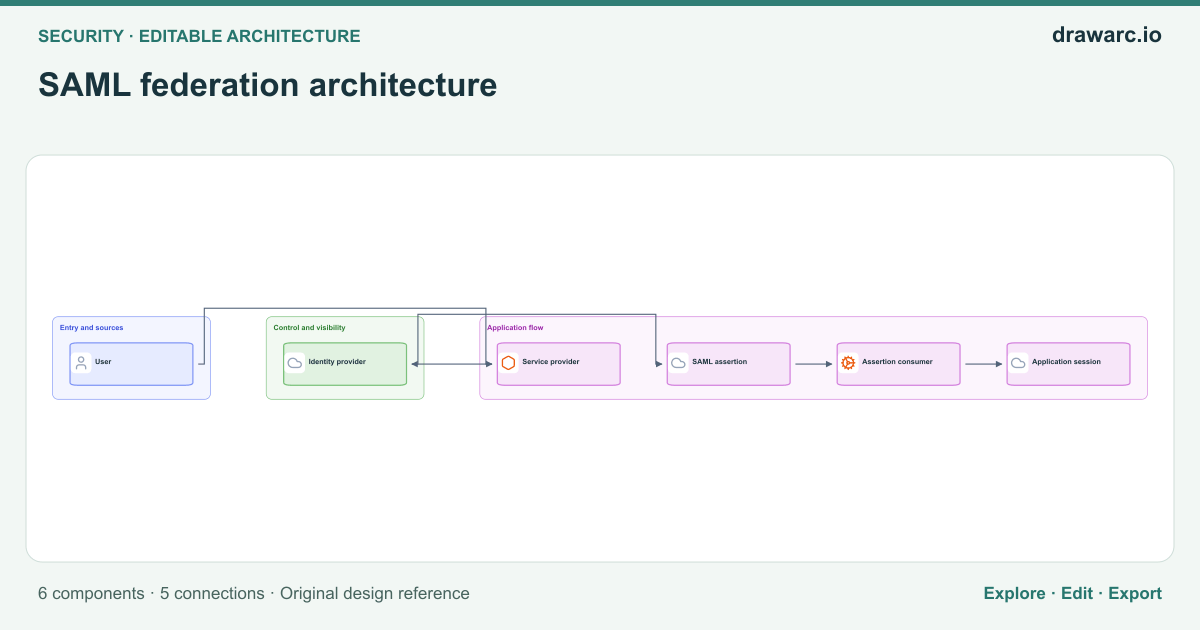
SAML federation architecture
Verify signatures and assertion audience and expiry.
6 components · 5 connections
Explore saml federation architecture →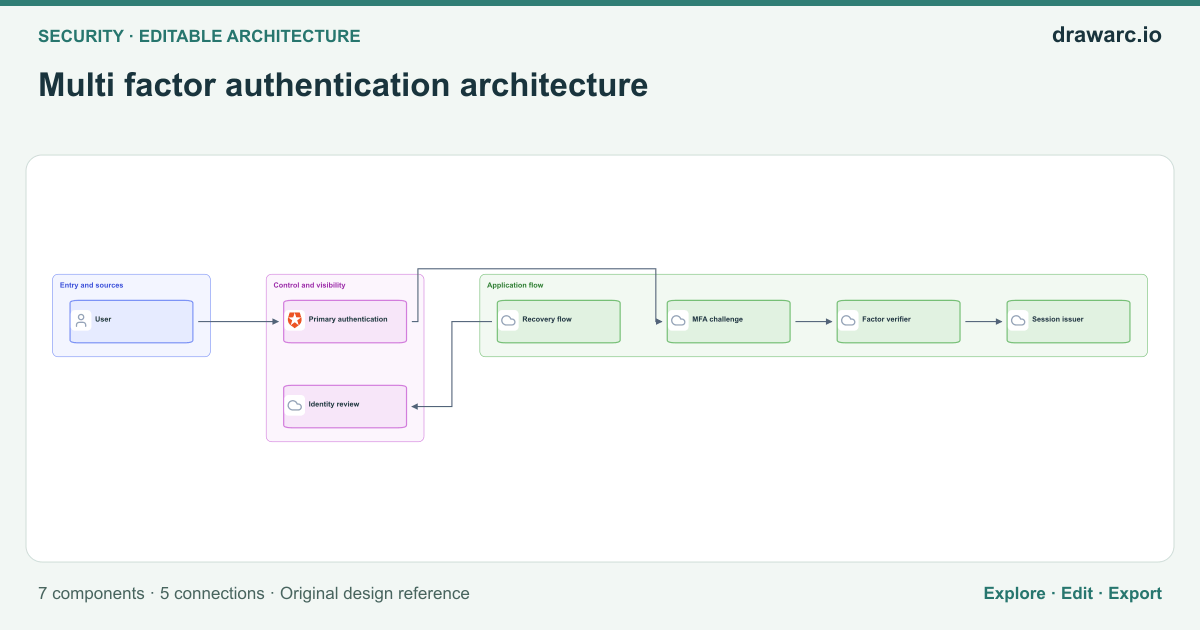
Multi factor authentication architecture
Recovery must not bypass factor security.
7 components · 5 connections
Explore multi factor authentication architecture →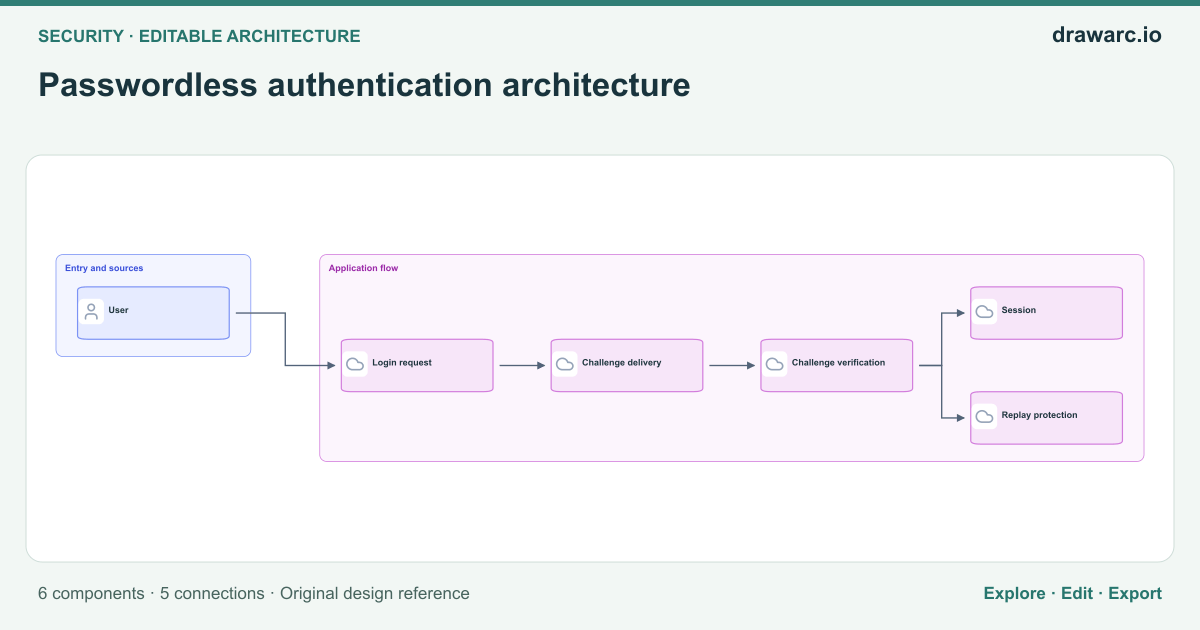
Passwordless authentication architecture
Bind challenges to identity and short expiry.
6 components · 5 connections
Explore passwordless authentication architecture →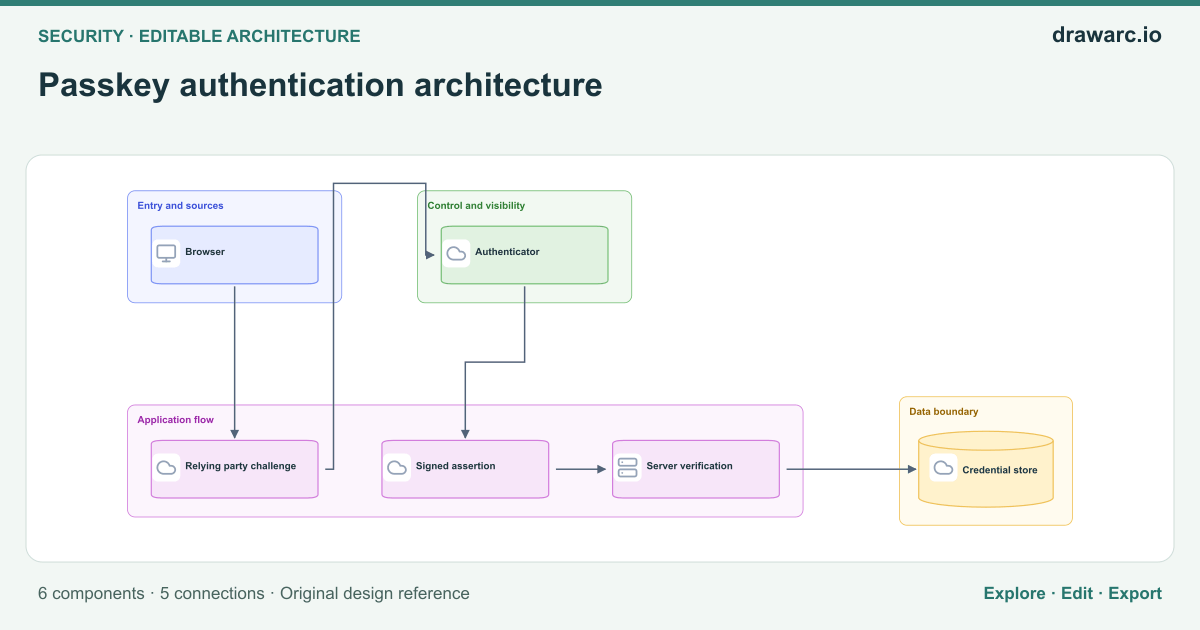
Passkey authentication architecture
Validate origin and relying-party identity.
6 components · 5 connections
Explore passkey authentication architecture →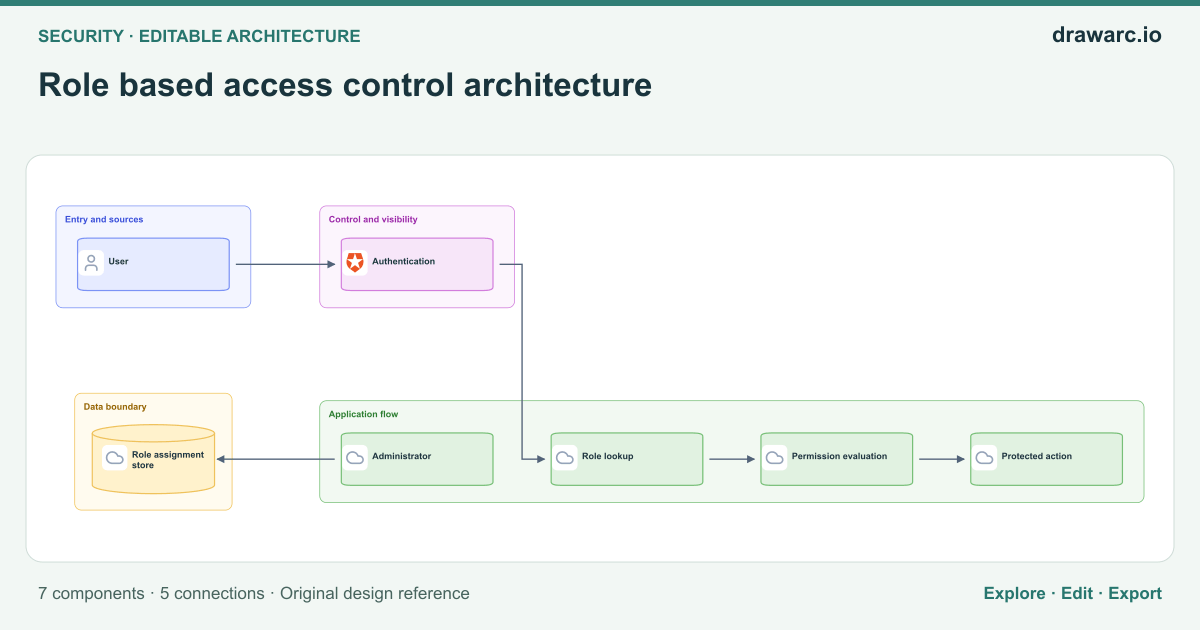
Role based access control architecture
Control who can assign privileged roles.
7 components · 5 connections
Explore role based access control architecture →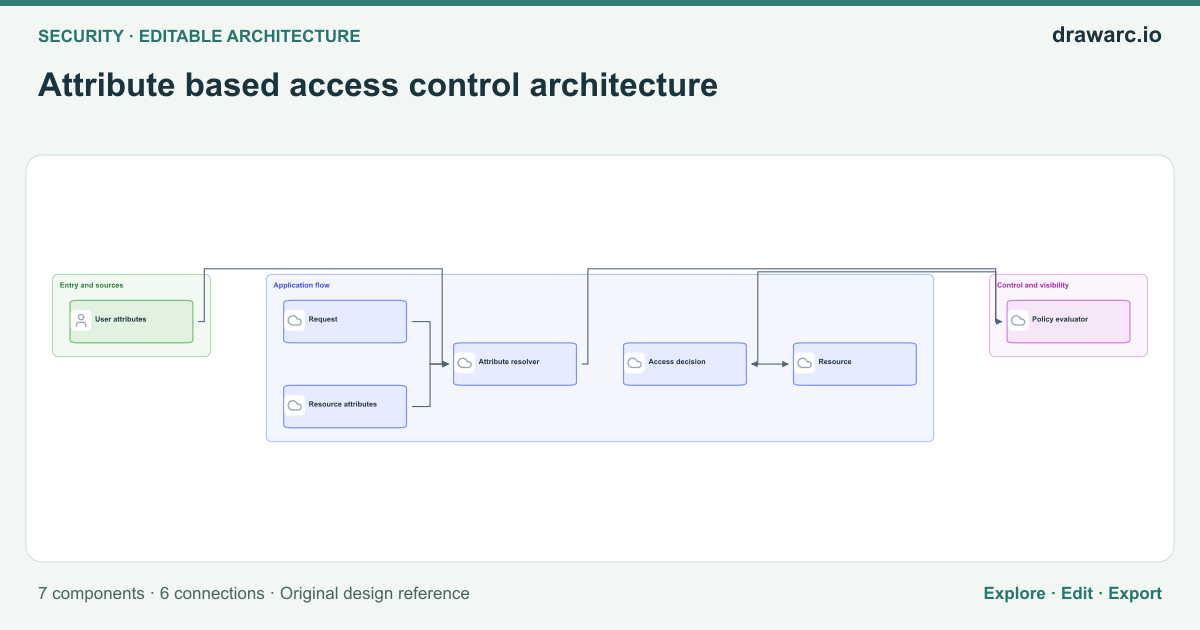
Attribute based access control architecture
Evaluate attributes from trusted sources.
7 components · 6 connections
Explore attribute based access control architecture →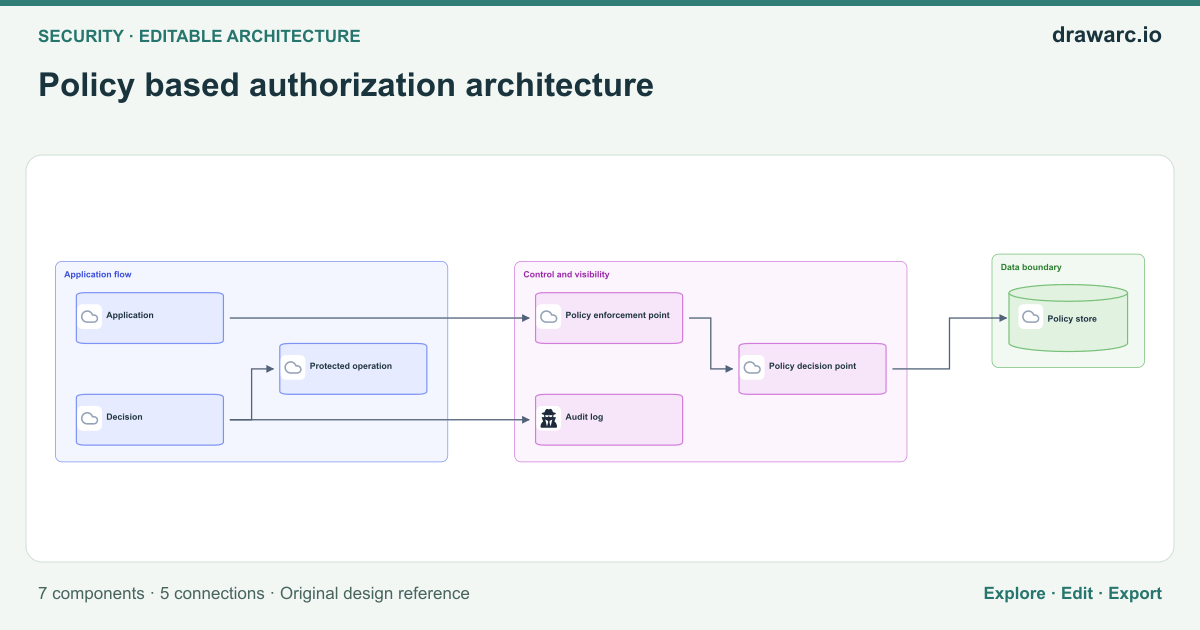
Policy based authorization architecture
Define behavior when the policy service fails.
7 components · 5 connections
Explore policy based authorization architecture →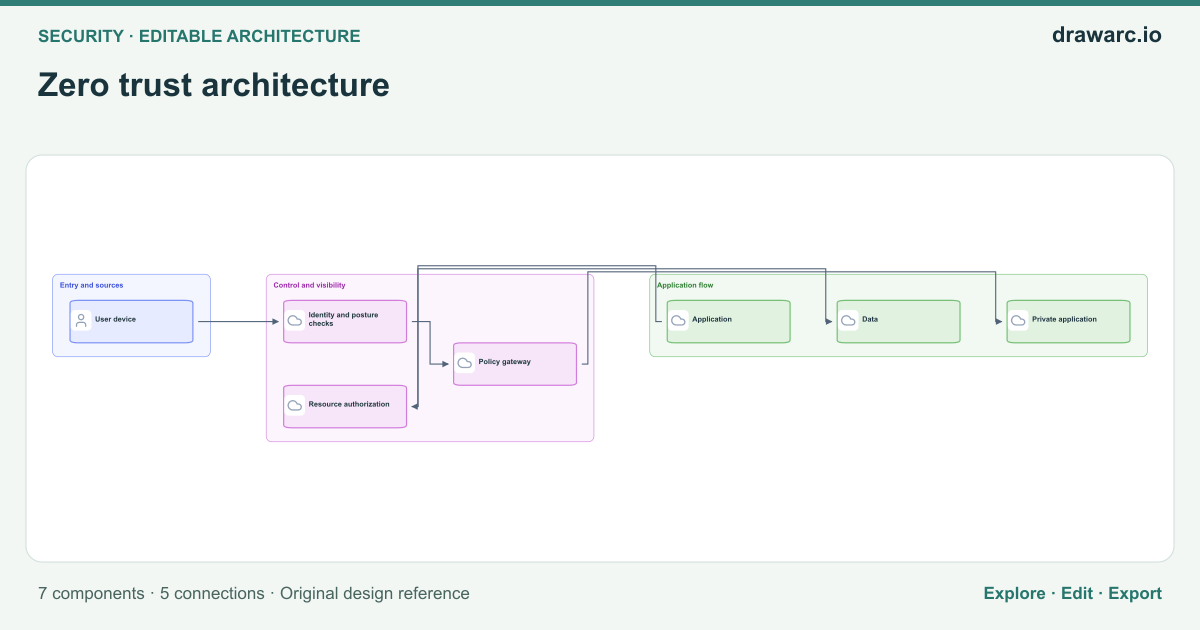
Zero trust architecture
Continuously evaluate access instead of trusting location.
7 components · 5 connections
Explore zero trust architecture →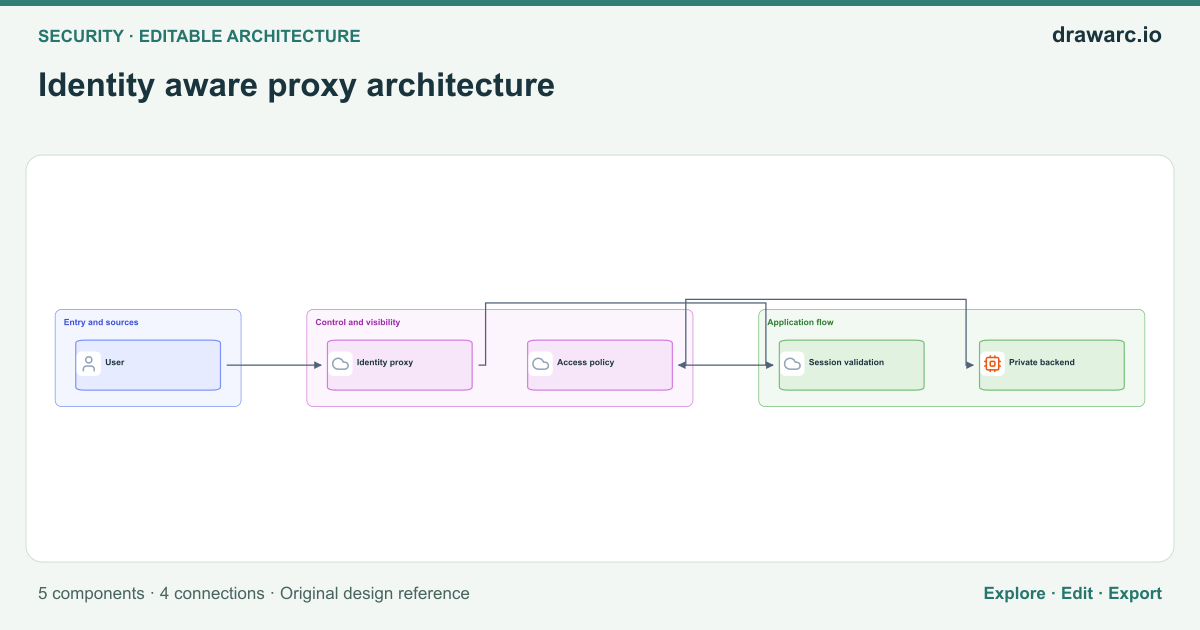
Identity aware proxy architecture
The backend must reject proxy bypass paths.
5 components · 4 connections
Explore identity aware proxy architecture →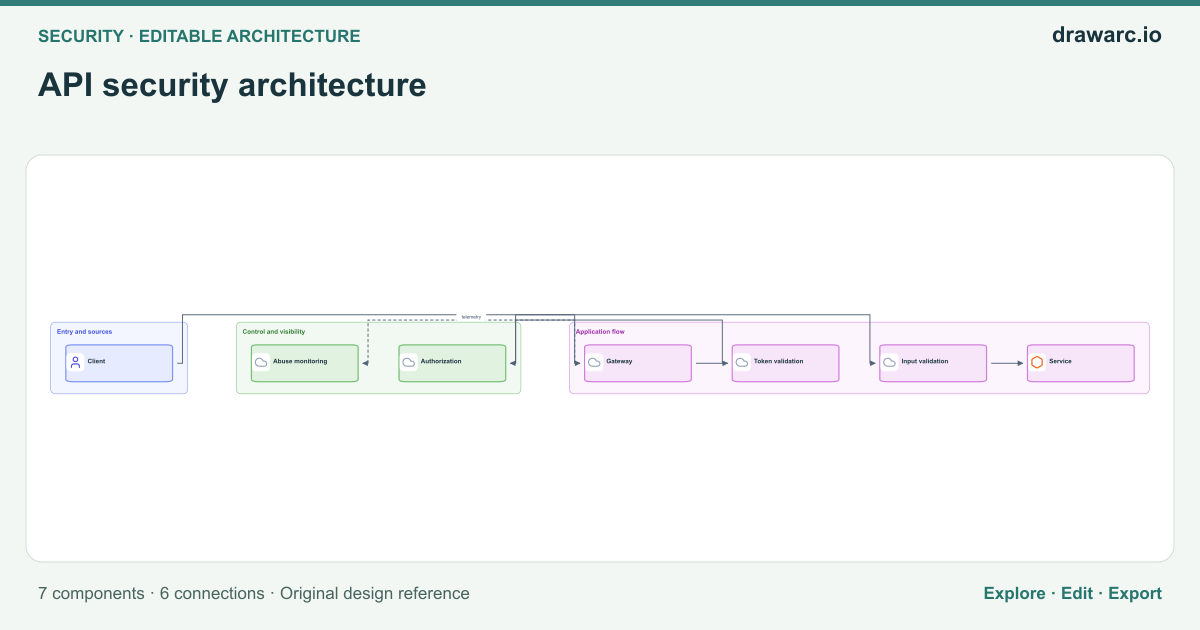
API security architecture
Identity checks do not validate business intent.
7 components · 6 connections
Explore api security architecture →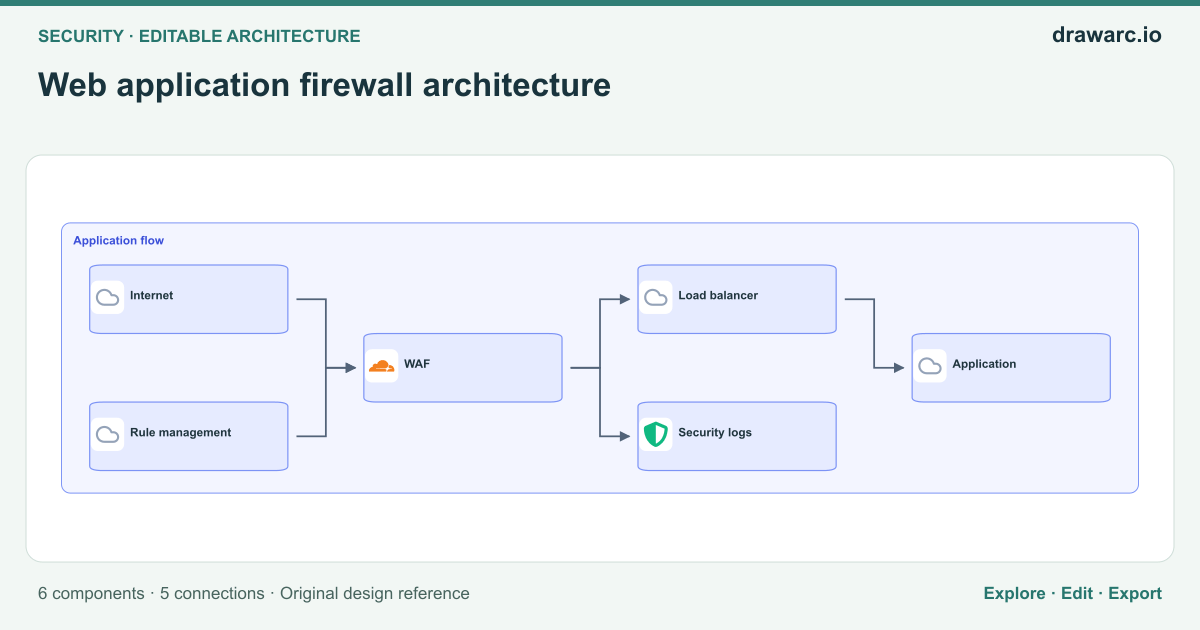
Web application firewall architecture
Tune rules without treating WAF as authorization.
6 components · 5 connections
Explore web application firewall architecture →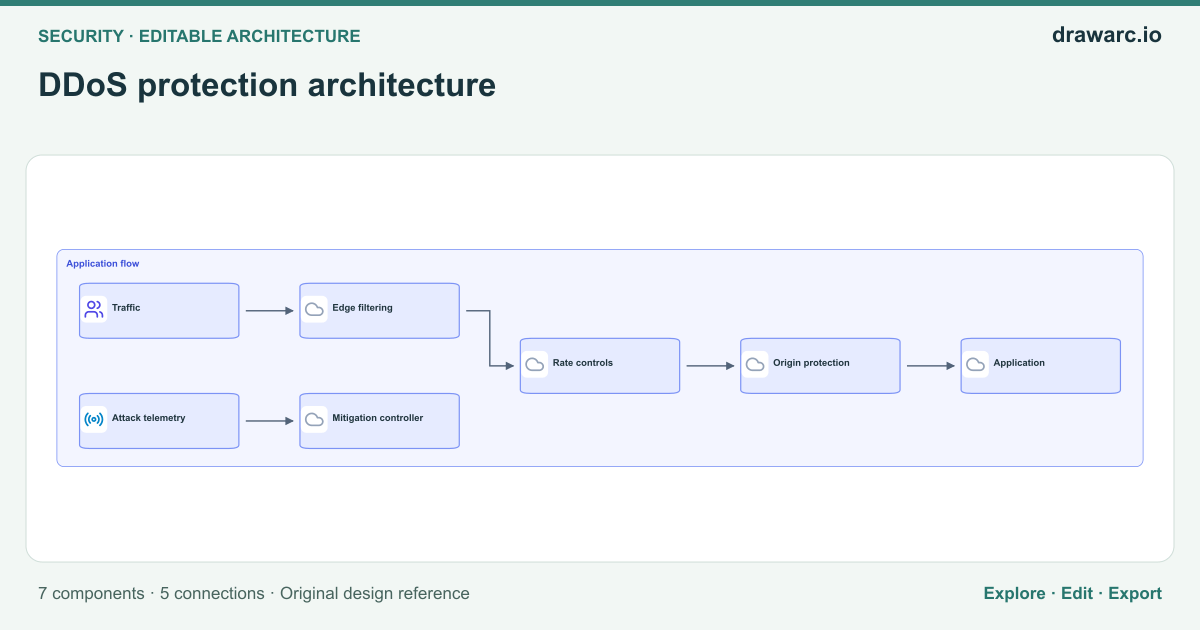
DDoS protection architecture
Protect origin paths from direct bypass.
7 components · 5 connections
Explore ddos protection architecture →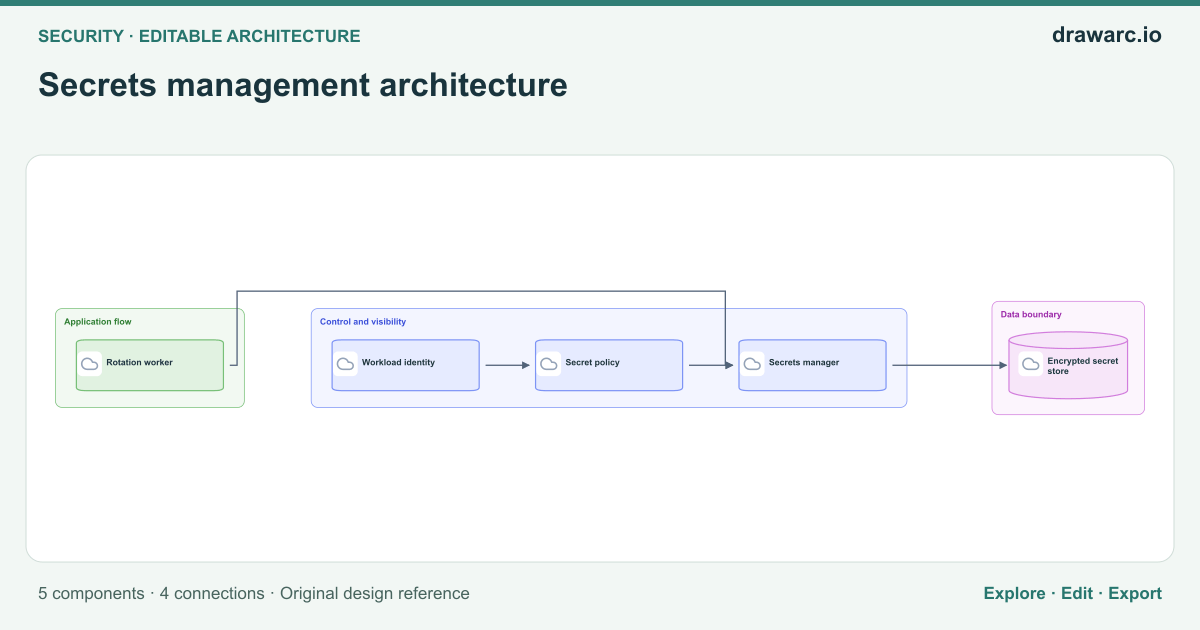
Secrets management architecture
Prefer short-lived credentials and controlled rotation.
5 components · 4 connections
Explore secrets management architecture →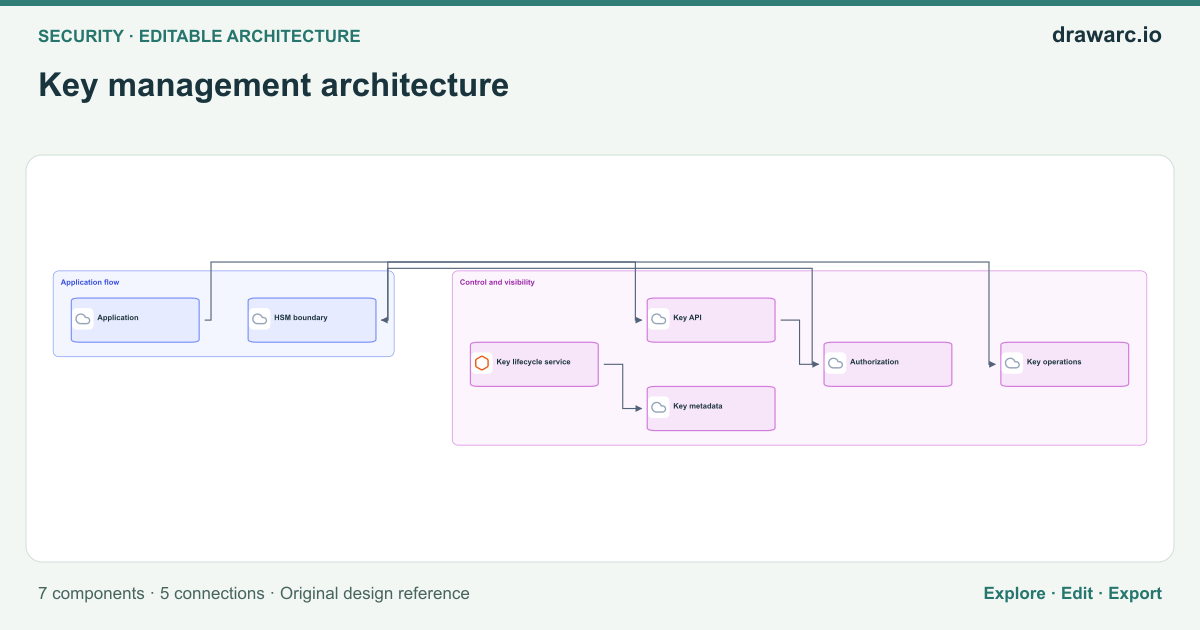
Key management architecture
Keep raw key material inside intended boundaries.
7 components · 5 connections
Explore key management architecture →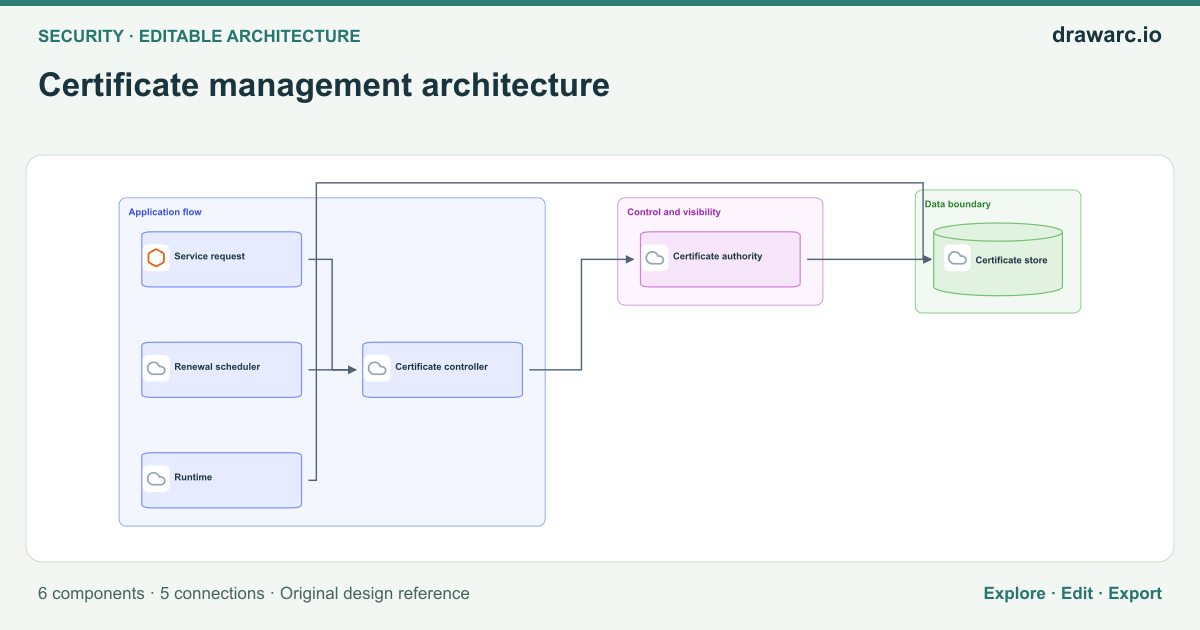
Certificate management architecture
Test renewal and revocation paths.
6 components · 5 connections
Explore certificate management architecture →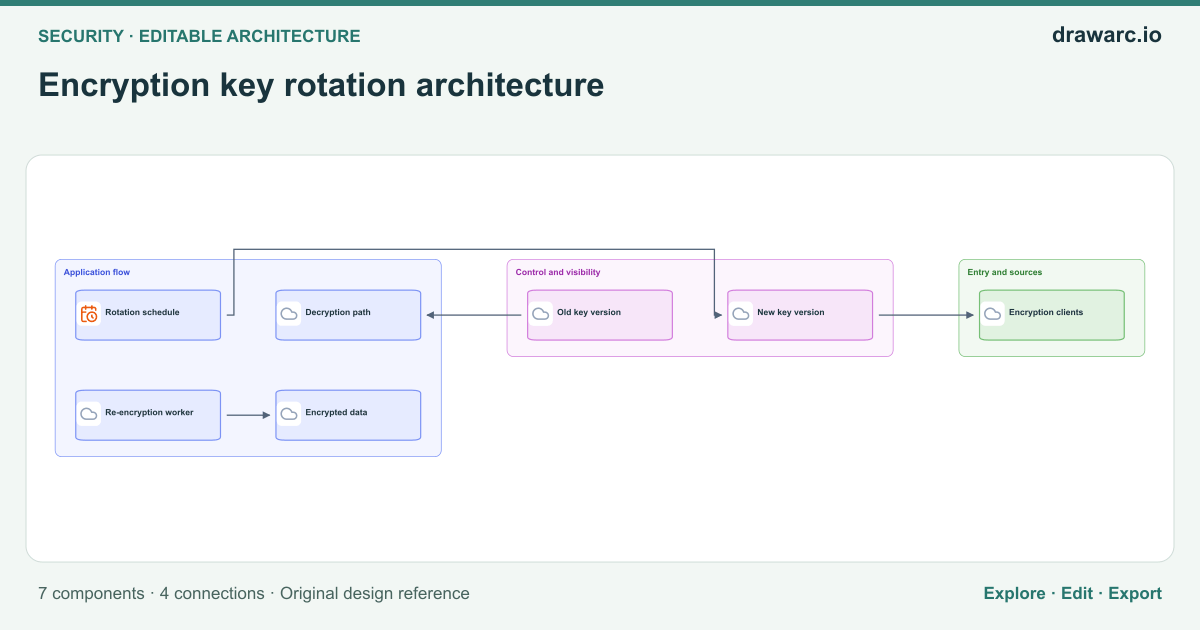
Encryption key rotation architecture
Do not retire keys before dependent data migrates.
7 components · 4 connections
Explore encryption key rotation architecture →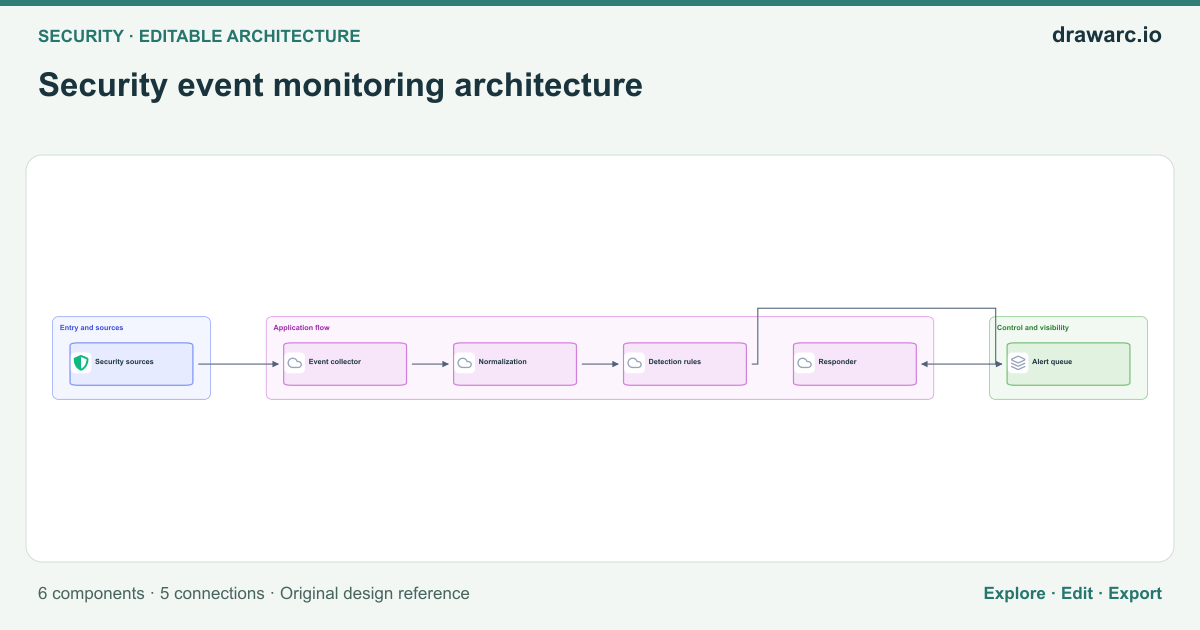
Security event monitoring architecture
Preserve event integrity and investigation access.
6 components · 5 connections
Explore security event monitoring architecture →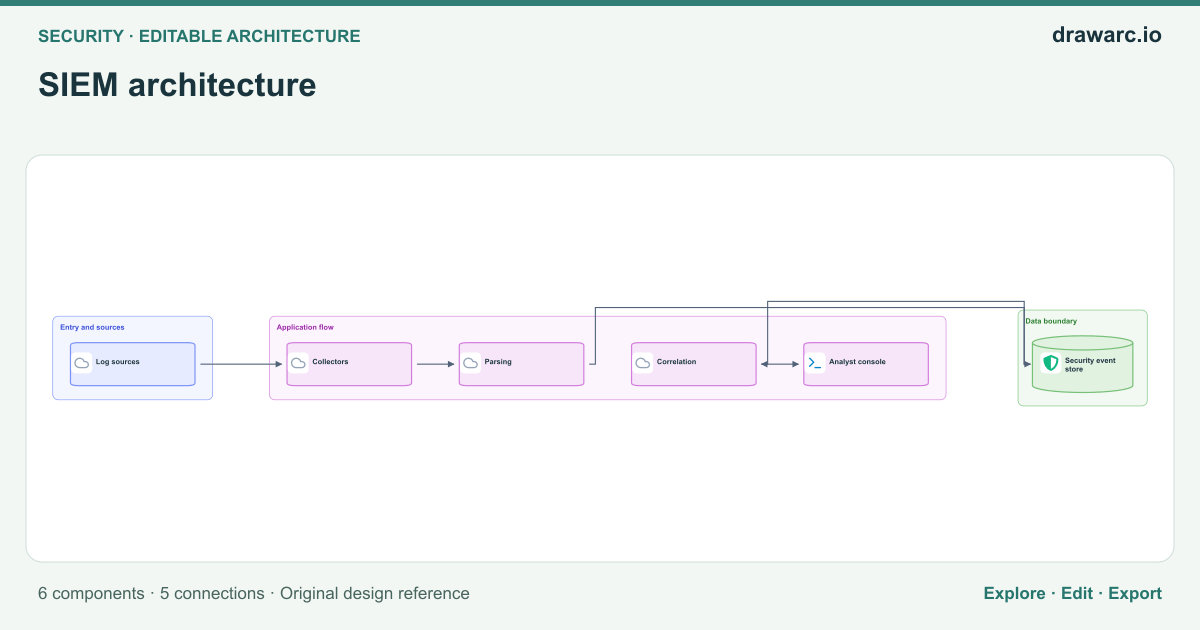
SIEM architecture
Control retention and sensitive-field exposure.
6 components · 5 connections
Explore siem architecture →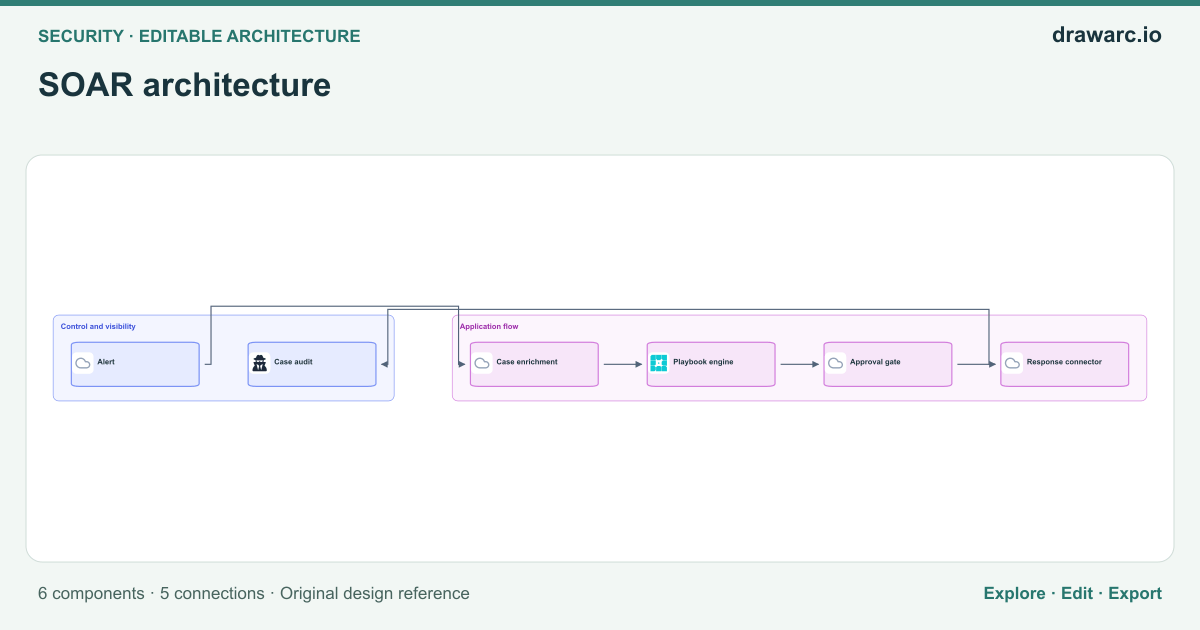
SOAR architecture
Automated response needs scoped execution permissions.
6 components · 5 connections
Explore soar architecture →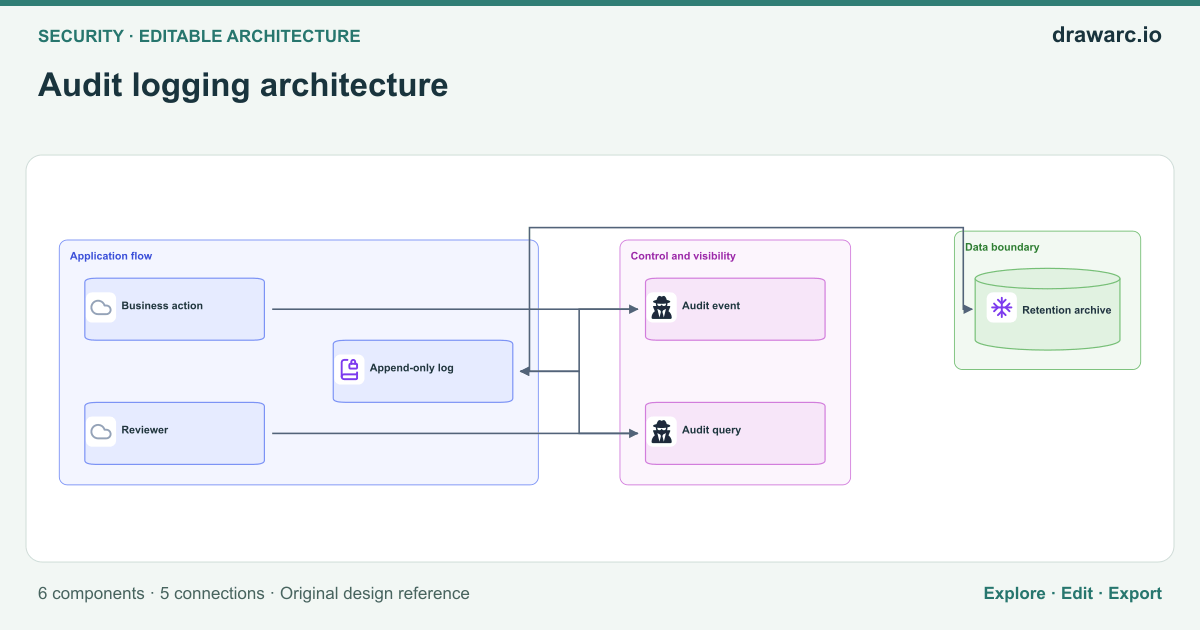
Audit logging architecture
Record actor and outcome without leaking secrets.
6 components · 5 connections
Explore audit logging architecture →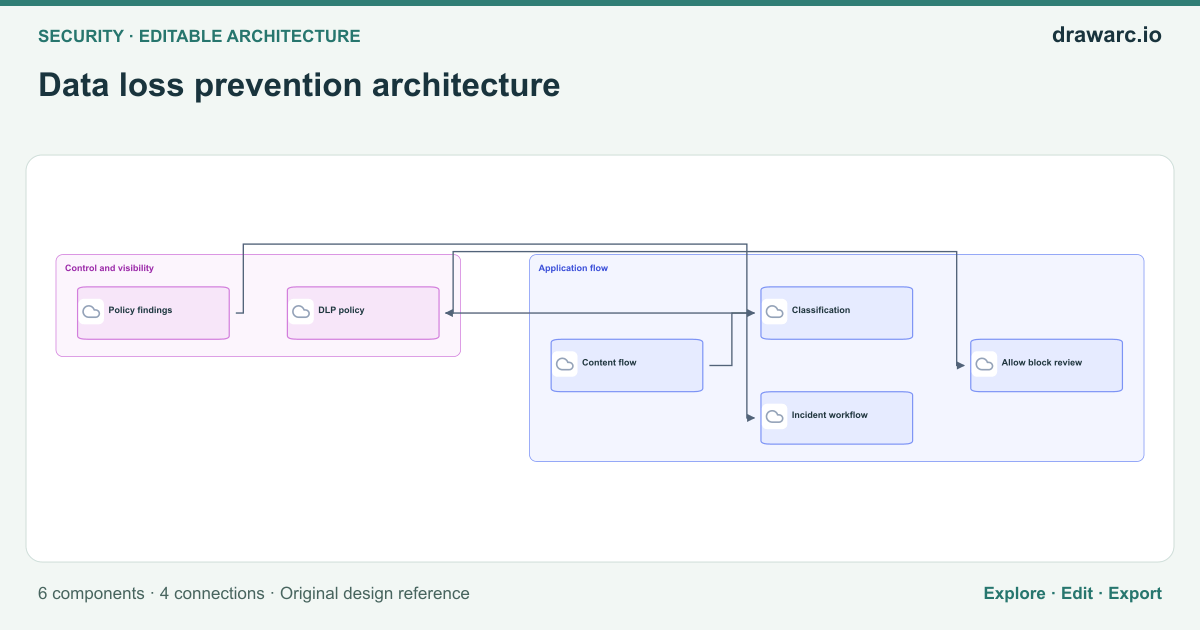
Data loss prevention architecture
Tune detection to avoid uncontrolled false positives.
6 components · 4 connections
Explore data loss prevention architecture →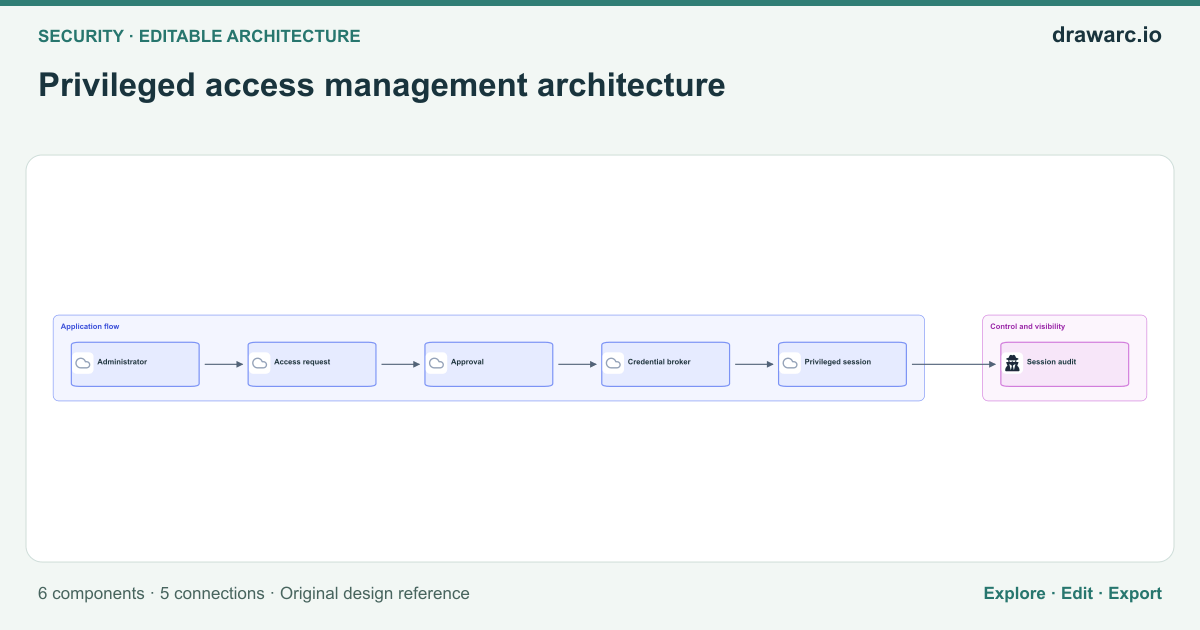
Privileged access management architecture
Grant time-limited privilege with traceability.
6 components · 5 connections
Explore privileged access management architecture →